For a cybersecurity governance course, I was asked to write a strategic report advising a hospital's board on artificial intelligence: where it strengthens their cybersecurity, where it makes things worse, and what a responsible rollout should actually look like. Healthcare felt like the right setting to take seriously, because a hospital's systems aren't just protecting data, they're connected to patient care itself.
AI cuts both ways, and the report treats that as the central problem rather than a footnote. Attackers now use generative AI to write phishing emails that read like genuine internal messages, and to fake voices or video for impersonation scams. Malware can adapt itself to dodge detection instead of relying on a fixed signature. On the defensive side, the same kind of technology, machine learning models trained on network and user behaviour, can catch anomalies that static, rule-based tools miss, and large language models can help a security team summarise and triage alerts faster.
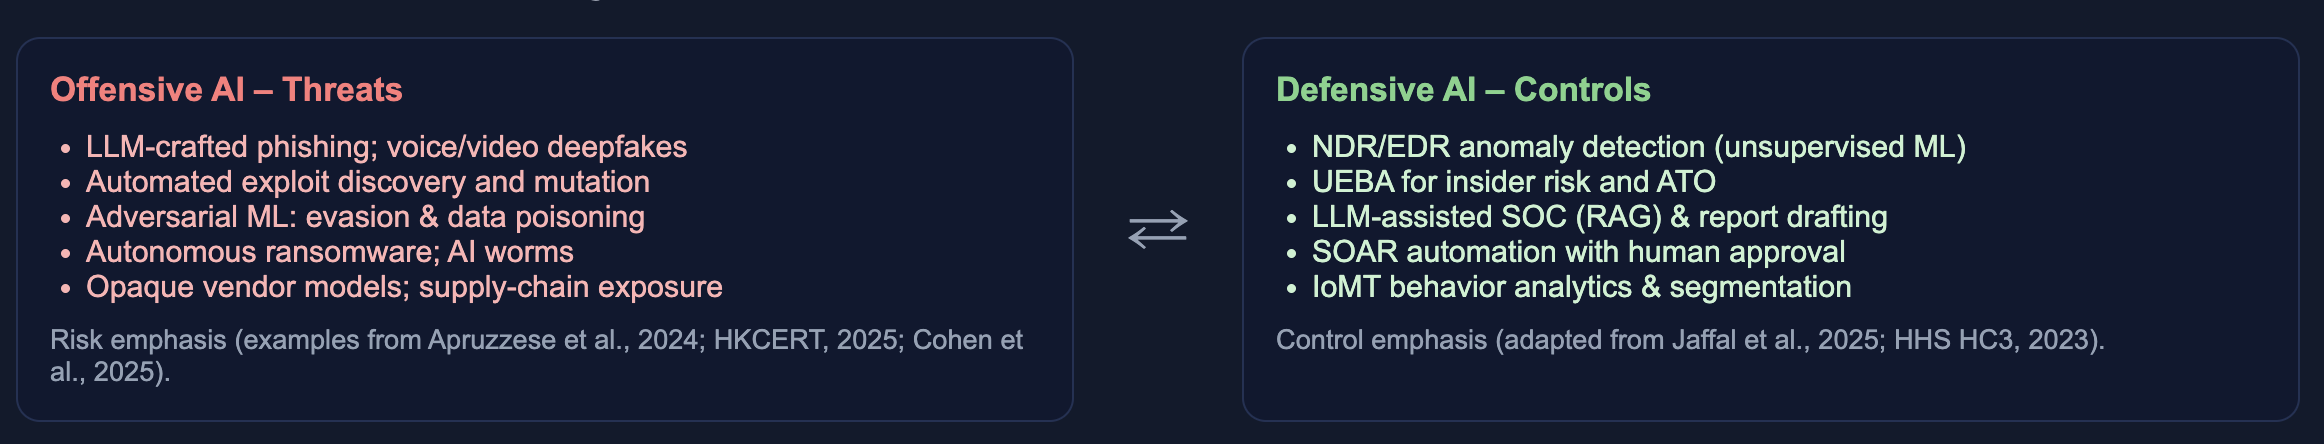
I didn't want the recommendation to just be "adopt AI tools." The report grounds every suggestion in existing governance frameworks, NIST's Cybersecurity Framework 2.0 and its AI Risk Management Framework, and ISO/IEC 27001 and 27701 for information security and privacy, so that any AI a hospital brings in stays accountable and auditable rather than a black box making decisions on its own.
The actual proposal is a four-phase rollout rather than a single deployment. Audit first: work out where the hospital's data, tooling and processes actually stand before touching anything. Pilot next: trial one AI capability, like anomaly detection on a limited, high-risk part of the network, with a human reviewing its output before anything is trusted at scale. Deploy follows only after the pilot proves itself, rolling out to other sensitive areas alongside staff training and privacy assessments. Monitor is ongoing after that: tracking things like detection and response times, retesting the models periodically, and keeping a standing oversight group across IT, clinical and compliance staff watching for the system drifting or behaving unexpectedly.
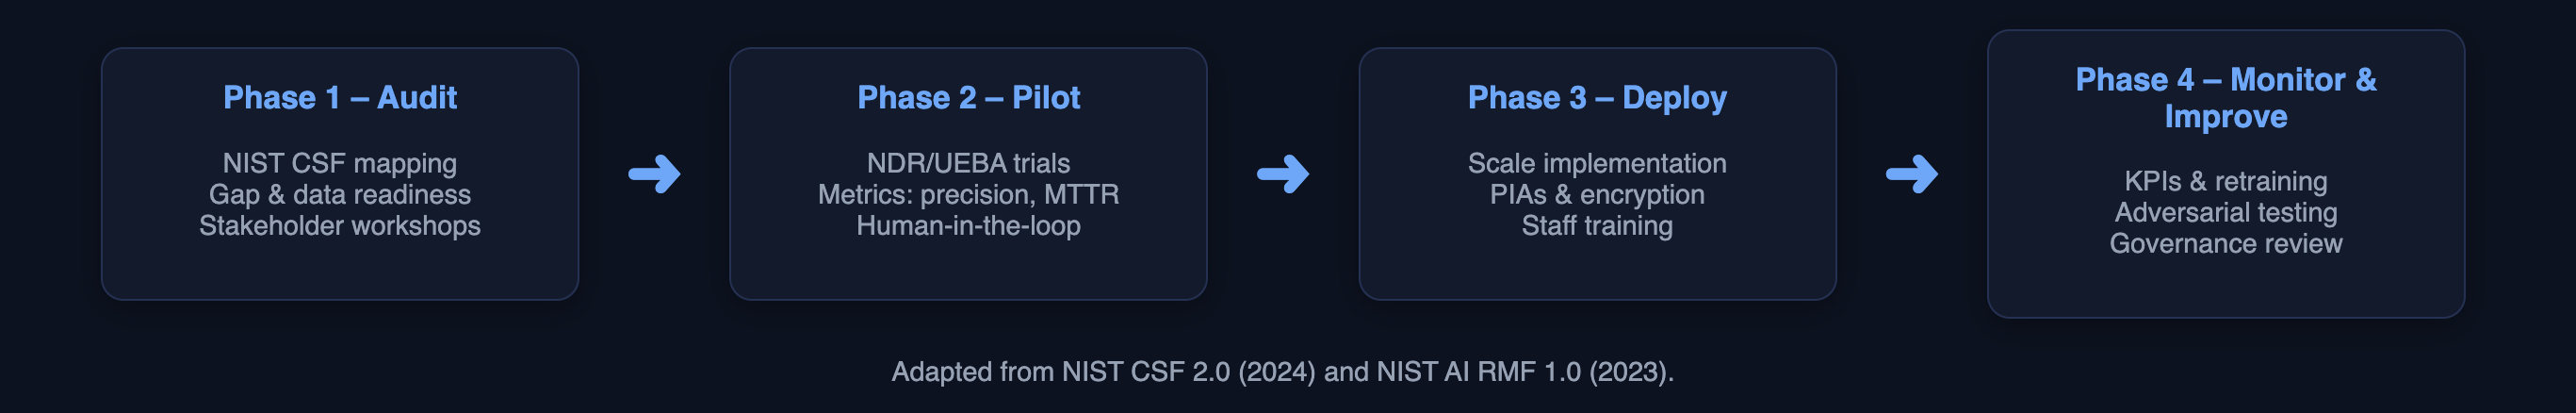
What mattered to me in this report wasn't listing impressive AI capabilities, it was building a case a hospital board could actually approve responsibly: AI treated as something that needs auditing and human oversight the whole way through, not a plug-and-play fix, in a setting where getting it wrong doesn't just mean a data breach, it can mean patient safety.